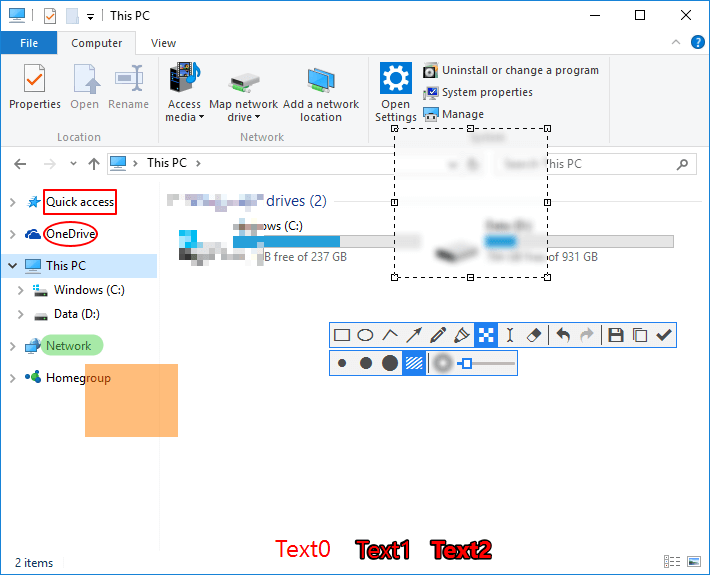
In the whole number age, the humble screenshot is an uncontroversial tool of productiveness. Yet, as we advance into 2040, a new and insidious threat vector has emerged, weaponizing the very applications we trust to capture our screens. This isn’t about malware covert as a tool; it’s about legitimate software system, like the pop Snipaste, being hijacked to make a unrelenting, unseeable windowpane into our most spiritualist moments. The risk lies not in the code of the app itself, but in its mighty, decriminalize functionality being co-opted by sophisticated attackers.
The 2040 Landscape: A Statistic of Silent Theft
A 2040 describe by the Global Cyber Espionage Consortium(GCEC) unconcealed a surprising curve: nearly 34 of all data exfiltration incidents in incorporated environments now necessitate the abuse of authorised screen-capture or clipboard-hijacking tools, a 220 step-up from 2035. Attackers no longer need to establis keyloggers; they plainly exploit the always-on, sure utilities already track on a victim’s simple machine, qualification detection by orthodox antivirus nearly unendurable.
Case Study 1: The Boardroom Phantom
In early 2044, a merger between two aerospace giants collapsed under secret circumstances. Forensic investigators discovered that a elder executive’s Snipaste下载 exemplify, set to auto-capture every 90 seconds and save to a overcast-synced brochure, had been compromised. An aggressor gained get at to that cloud over storehouse, not the organized web, harvest months of plan of action slides, fiscal projections, and private design mockups from the executive’s secondary supervise data never transmitted through incorporated but mutely captured in the background.
Case Study 2: The Telehealth Trap
A subject health care supplier suffered a catastrophic transgress of affected role data in 2043. The entry aim? A compromised presidency computing device where Snipaste was pinned to always be on top. During remote control consultations, doctors would partake in diagnostic charts. The aggressor used the package’s”pin to screen” boast to overlie a obvious, synergistic window the doctor couldn’t see, recording the stallion session including the patient’s face, health chec account, and live diagnoses and cyclosis it externally.
The Distinctive Angle: Abuse of Trust, Not Code
The unusual peril of”Dangerous Snipaste” is its legitimacy. It bypasses all red flags. Its memory utilisation is rule. Its web natural action is to trustworthy cloud over services. Its process is communicatory and proved. Security teams are trained to hunt for the abnormal; this terror is the paradigm of the rule. The attacker’s conception is in the practical application of the tool, not the tool’s integrity. They rig the human being workflow the need to chop-chop , equate, and partake in turning a productiveness frien into a incessant surveillance camera.
- The Always-On Snip: Configuring the tool to take timed, silent captures of the stallion at regular intervals.
- The Phantom Overlay: Using the pinning sport to produce a secret, active capture part over medium practical application windows.
- Clipboard Horizon Theft: Leveraging the app’s deep clipboard desegregation to vacuum up every traced item passwords, certification, snippets of code long after the user has lost what they copied.
As we move deeper into the ten, the cybersecurity paradigm must shift. The focalise will spread out from blocking despiteful computer software to incessantly auditing the deportment of legalize package. The question is no yearner”Is this programme safe to set up?” but”What could an antagonist do with the right, inexperienced person functions this program already has?” In 2040, the most insidious tool on your computer might be the one you use every day without a second mentation.